On October 30, 2026, the global cryptocurrency industry was rocked by an unprecedented security breach targeting Binance, the world’s largest digital asset exchange by trading volume, in which threat actors siphoned off a total of $6.36 billion in crypto assets across 10 separate blockchains in a span of just 20 minutes. The platform immediately paused all user withdrawal services for the 20-minute window to contain the breach shortly after detecting the anomalous wallet activity. In a rapid coordinated response, Binance’s internal security teams froze roughly $3 billion of the misappropriated funds, while leading stablecoin issuers Tether and Circle collaborated with investigators to seize an additional $2.3 billion in stolen assets, according to Reuters reporting. Leading blockchain forensics firms TRM Labs and Chainalysis have independently traced the sophisticated heist to TraderTraitor, a well-documented hacking subgroup under North Korea’s notorious Lazarus Group, a cyber espionage and financial crime collective long tied to state-sponsored operations. For decades, independent cybersecurity analysts have confirmed that proceeds from such crypto heists are diverted to fund the isolated nation’s banned nuclear and ballistic missile development programs, though North Korean officials have consistently issued blanket denials of any involvement in hacking activities. At the time of publication, Binance’s internal probe has not yet publicly named the perpetrator group, and the U.S. Federal Bureau of Investigation alongside the U.S. Secret Service have formally launched a joint federal investigation into the massive breach. The scale of the theft far outstrips the prior all-time record for a crypto heist, the $1.5 billion breach of rival exchange Bybit that took place in February 2025. News of the historic hack sent shockwaves across global digital asset markets, driving leading cryptocurrencies Bitcoin and Ether down to multi-week price lows in hours. Binance leadership has issued a public assurance that no end user will face financial losses from the incident, committing to fully cover any unrecovered stolen funds out of its own reserves, and confirmed that it is coordinating in real time with global law enforcement agencies to trace and recoup the remaining outstanding stolen assets, with full resumption of all withdrawal services scheduled to take place within 45 hours of the breach detection.
分类: technology
-
COMMENTARY: AI becomes part of the tourism demand
A largely overlooked, high-stakes challenge powered by artificial intelligence is quietly reshaping the competitive landscape for Caribbean nations whose economic survival is deeply tied to tourism revenue. For decades, regional tourism boards, hotel operators, airline carriers, and airport authorities have directed nearly all their marketing efforts toward directly capturing the attention of human travelers, investing millions in splashy ad campaigns, influencer partnerships, and traditional branding pushes designed to stand out amid a crowded global travel market. But as traveler behavior rapidly evolves, that long-standing playbook is growing increasingly obsolete: modern travelers are no longer sifting through hundreds of search engine results or directly visiting tourism board websites to plan trips, they are turning to generative AI tools to curate their travel shortlists for them. This paradigm shift means Caribbean destinations no longer only need to compete for the notice of human vacationers — they now must compete to be prioritized in the recommendation sets that AI systems generate for users. Unlike traditional travel platforms that return long lists of links for users to explore independently, today’s AI-mediated travel tools process thousands of data points in seconds to deliver a narrow, pre-vetted set of destination options, effectively deciding which locations even enter a traveler’s initial consideration pool before that person has done any independent research of their own. The scale of this shift is already measurable: a 2026 global travel industry survey found that 54% of all travelers have already used AI tools to plan trips, 40% have discovered a new travel destination through an AI recommendation, and 29% have completely altered their original travel plans after receiving a suggestion from an AI platform. Shockingly, however, only 26% of surveyed destination marketing organizations worldwide have a formal, documented AI integration strategy — a gap that creates acute, disproportionate vulnerability for Caribbean economies that rely almost entirely on tourist spending to sustain local jobs and public services. Additional data shows that the top five most digitally visible global travel destinations already capture 38% of all AI-generated travel recommendations, creating a self-reinforcing advantage that locks out lesser-known locations with weaker digital footprints. Critically, AI recommendation algorithms do not prioritize destinations based on how much money they spend on paid advertising. Instead, these systems synthesize a vast cross-section of publicly available digital data to build their understanding of a location, drawing from third-party travel publications, verified guest reviews, structured datasets of local attractions and transportation links, social media discussions, peer travel blogs, and official public records, rather than just the polished promotional copy hosted on a destination’s official tourism website. Recent peer-reviewed academic research confirms that destinations with rich, diverse, and widely distributed authoritative digital content are far more likely to be included in AI recommendation shortlists, while even naturally stunning, visitor-friendly Caribbean islands can be entirely excluded from AI-generated consideration sets if their digital representation is sparse, outdated, or limited only to their own official marketing materials. This is no longer a minor marketing technicality: for tourism-dependent Caribbean islands, building out a comprehensive, structured digital evidence base that AI systems can crawl and interpret accurately has become a core economic development priority, not just a branding side project. Without proactive action to boost their AI discoverability, even Caribbean destinations with world-class beaches, unique cultural experiences, and premium hospitality offerings risk being systematically overlooked by AI tools, as algorithms unintentionally amplify the visibility of competing destinations that have already invested in robust digital representation. Industry analysts urge regional tourism authorities to elevate AI discoverability to the same priority level as their long-standing traditional advertising, social media, and branding campaigns, noting that prioritizing diverse, third-party validated digital content will be critical to safeguarding the Caribbean’s $60 billion annual tourism sector from AI-driven market concentration in the coming years.
-
Antigua and Barbuda Unveils Plan to Improve Government Services and Access to Information Online by 2030
Following two years of cross-stakeholder collaborative drafting that kicked off in 2022, the twin-island nation of Antigua and Barbuda, in formal partnership with the United Nations Development System, has officially rolled out its comprehensive national Digital Transformation Strategy alongside a dedicated public-facing digital portal, laying out a structured, actionable roadmap to steer the country’s digital advancement through to 2030.
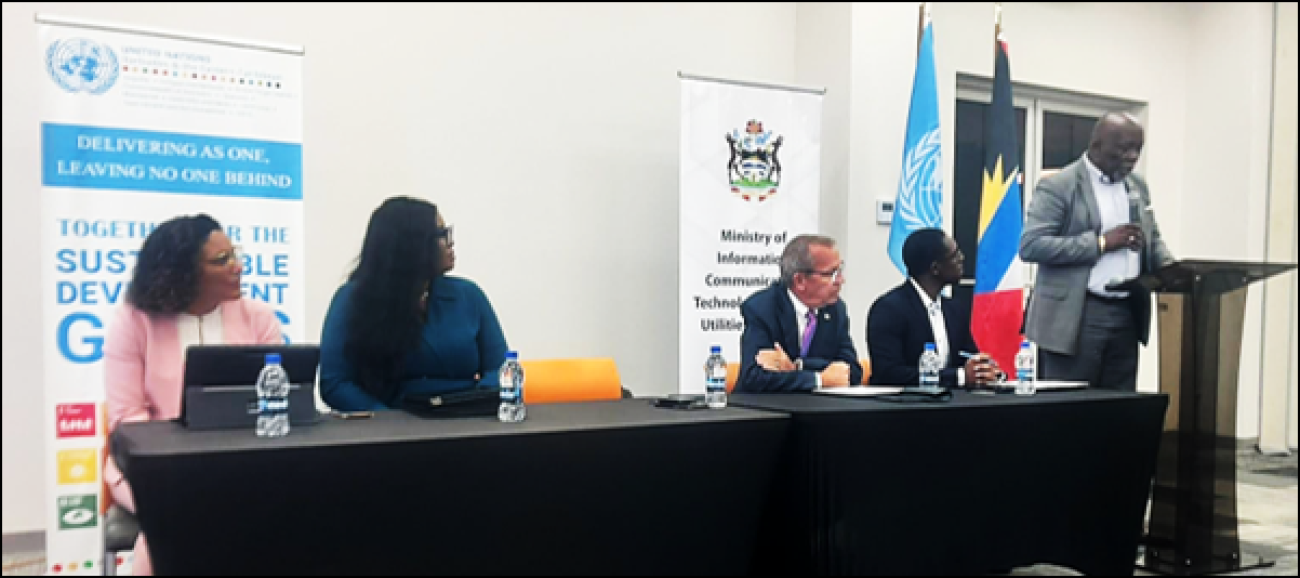
The landmark hybrid launch event brought together a wide coalition of partners spanning government agencies and multiple UN entities, including the UN Resident Coordinator’s Office, UNESCO, UNDP, PAHO, ITU, UNICEF, and UN Women, to mark the end of a multi-year co-development process and the official start of national implementation efforts.
Presiding over the launch, Honourable Melford Nicholas, the nation’s Minister of Information and Communication Technologies and Energy, delivered a formal public commitment to full execution of the strategy by the 2030 target date, while extending sincere gratitude for the robust, five-year collaborative support the UN Development System has provided to lay the groundwork for the digital modernization agenda.
Structured to deliver tangible, inclusive progress, the strategy is built around a three-phased implementation framework anchored to 10 high-priority targeted projects, all designed to elevate Antigua and Barbuda into a digitally advanced, adaptive, and resilient small island developing state.
Event speakers repeatedly emphasized that successful digital transformation cannot be delivered by government acting in isolation. Andrea Andrew, Antigua and Barbuda Country Coordinator, stressed that the national digital ambition requires coordinated, cross-sector buy-in from private industry, academic institutions, civil society groups, global development partners, and ordinary citizens across the islands.
This collective partnership ethos was echoed by Simon Springett, UN Resident Coordinator for Barbados and the Eastern Caribbean, who noted that years of joint work between UN agencies, national government teams, and local stakeholders had positioned digital transformation as a core enabler of the country’s broader sustainable development goals. “Today’s launch is not the conclusion of a process; it is, in many critical respects, the starting line,” Springett stated, before formalizing the UN Development System’s pledge to deliver ongoing implementation support, including specialized technical expertise, multi-stakeholder partnership facilitation, and access to global innovation networks and leading industry knowledge.
A key tangible output unveiled at the event is the official Digital Transformation Webpage, a purpose-built public platform designed to expand equitable public access to government information and services. Eric Falt, Regional Director of the UNESCO Regional Office for the Caribbean, highlighted the direct link between open digital access to information, civic empowerment, and meaningful public participation in governance. He noted that the new platform aligns fully with the core principles of Antigua and Barbuda’s Freedom of Information Act, ensuring residents can access clear, timely, and verified data about government services and policy decisions to better exercise their civil rights and engage with public institutions. The portal is built with full accessibility features for marginalized users, and a step-by-step video navigation guide was premiered during the launch to help all residents easily navigate its functions.
Isoke Perry, the national Digital Transformation Focal Point and Director of E-Government, welcomed the strategy’s deliberate action-oriented structure, noting that the phased roadmap and 10 priority projects will provide clear, consistent guidance to move the twin-island nation steadily toward its digital modernization and resilience goals. Perry also formally launched the Antigua and Barbuda Digital Transformation Journey, a public timeline that documents all key milestones of the country’s digital evolution to date, an initiative led by UNESCO in partnership with the Ministry of ICTs and Energy and the UN Resident Coordinator’s Office.
Don Charles delivered a detailed walkthrough of the full strategy and its decade-long 10-project implementation timeline, followed by structured feedback sessions that centered underrepresented stakeholder voices, including youth representatives, private sector leaders, people living with vulnerabilities, and civil society organizers, to ensure the implementation process responds to the full range of community needs. Additional speakers outlined targeted support commitments from partner bodies: Jordanna Straker, Caribbean Subregional Coordinator for UN Volunteers, laid out the organization’s dedicated digital transformation support agenda and specific areas where UN Volunteers personnel will contribute to local execution efforts, while Arita Phillip, Associate Programme Specialist for Communication and Information at UNESCO, led a guided review of the full strategy document and new public webpage. Kenroy Roach, from the UN Resident Coordinator’s Office for Barbados and the Eastern Caribbean, delivered the event’s closing remarks, calling for sustained collective commitment across all participating groups.
The hybrid launch drew hundreds of in-person and virtual attendees from national government bodies, UN agencies, and intergovernmental organizations across the region. With the formal rollout of the full strategy, priority project list, phased implementation roadmap, and public digital portal complete, national efforts are now fully focused on translating Antigua and Barbuda’s forward-looking digital ambitions into tangible, inclusive on-the-ground outcomes over the next seven years. -
COMMENTARY: AI becomes part of the tourism demand
For decades, the global tourism industry has evolved in lockstep with technological progress, from the rise of online booking platforms in the 1990s to the widespread adoption of digital travel passes and contactless services following the 2020 pandemic. Today, a transformative new shift is reshaping consumer expectations and industry operations: artificial intelligence has moved from a niche experimental tool to a non-negotiable component of modern tourism demand. This commentary explores the multifaceted ways AI is redefining both what travelers expect from their journeys, and how hospitality and travel providers are adapting to meet these new requirements. Travelers across all demographic segments are increasingly prioritizing AI-powered features when planning trips, according to recent 2024 consumer surveys from leading global travel associations. Gen Z and millennial travelers, who make up 60% of global international travel spending, now regularly use AI chatbots to generate personalized itinerary suggestions that align with their specific budget constraints, dietary restrictions, and off-the-beaten-path preferences, rather than relying on pre-packaged generic tour bundles that dominated the market a decade ago. Even older traveler demographics are embracing AI tools, using real-time language translation AI integrated into hotel apps to navigate unfamiliar destinations, or AI-powered accessibility tools that adjust travel plans to accommodate mobility limitations in real time. On the supply side, tourism operators from small family-run bed and breakfasts to multinational hotel chains and major airline groups are integrating AI systems not just to cut operational costs, but to meet the rising baseline of customer demand. AI dynamic pricing tools allow properties to adjust rates in real time to match fluctuating local demand, while AI-powered customer service assistants resolve common traveler queries – from check-in adjustments to local restaurant recommendations – in seconds, eliminating long wait times that were a longstanding pain point for the industry. This shift is not without its growing pains: industry stakeholders note that providers must balance AI deployment with personalized human interaction to avoid eroding the warm, experiential core that draws people to travel in the first place. But the broader trend is irreversible: AI is no longer a flashy optional add-on for tourism brands, it is a fundamental element of what travelers now consider a high-quality, seamless travel experience.
-
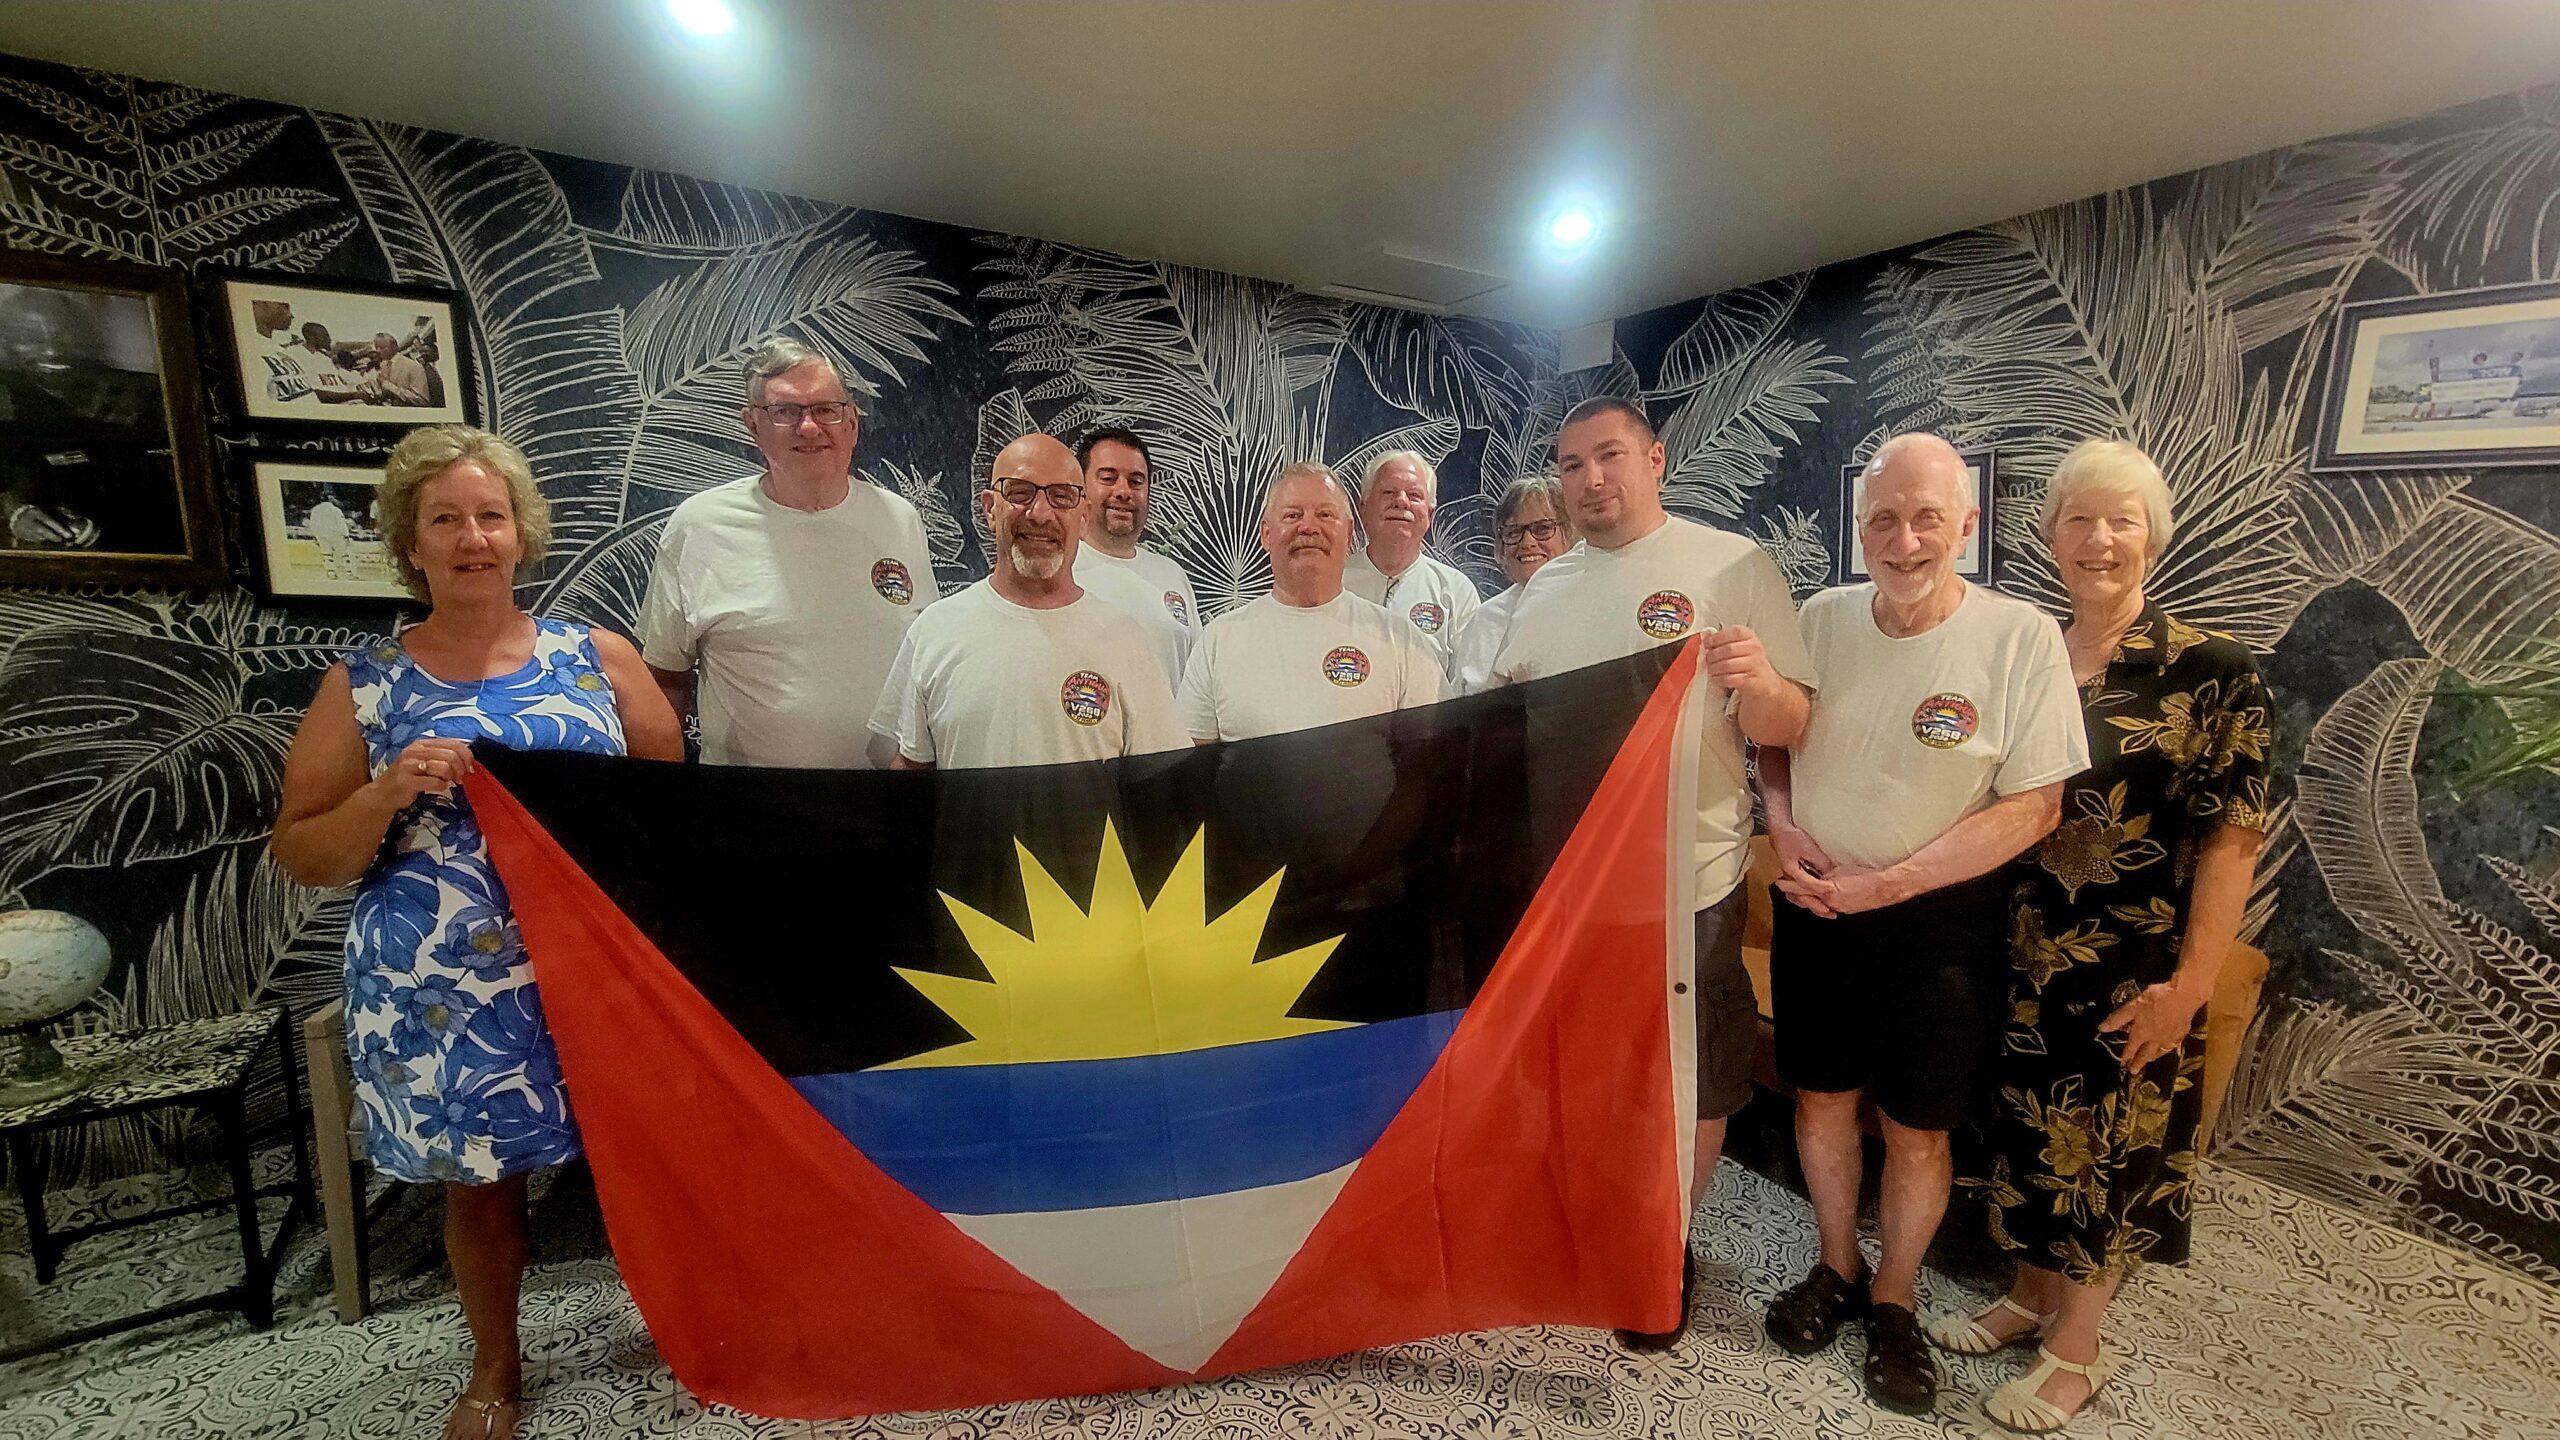
Team Antigua Claims Top North American Spot and Second Worldwide in Ham Radio Competition
A cohort of international and local amateur radio, widely known as “ham radio,” enthusiasts descended on Antigua over the recent weekend to take part in the iconic annual CQ Worldwide Ham Radio Contest, one of the most prestigious long-running events in the global shortwave operating community. The annual competition draws tens of thousands of licensed ham operators across every inhabited continent, challenging participants to log as many verified two-way shortwave contacts as possible, with extra points awarded for connecting to operators in distinct, geographically dispersed nations. As the official and only registered team representing Antigua in this year’s contest, the group’s operating location on the Caribbean island made it an extremely high-priority target for competing operators worldwide, who often spend months planning their contest operations to secure contacts with rare or underrepresented geographic locations to boost their final scores. Dubbed Team Antigua, this dedicated collective has made the annual pilgrimage to the island for this exact competition for 33 consecutive years, launching their first local operating setup at Long Bay back in 1993, and now running their high-power shortwave transmission hub from a purpose-built station in the Gunthorpes district. The team’s membership is deliberately inclusive: while the core cohort is made up of seasoned ham operators traveling from the United States, the group actively recruits participants from a broad range of other nations, as well as local Antiguan amateur radio license holders to join their annual operating effort. This year, the team logged an extraordinary total of more than 12,500 verified two-way shortwave connections, successfully reaching operators in 154 separate countries spanning every major global region, including Japan, Australia, Russia, China, the contiguous United States, all of the European continent, the broader Caribbean, India, and every populated region in between. Based on their submitted real-time operation logs, the team projects they have secured first place in the North American division and an impressive second-place finish in the global overall rankings, though official final results will not be confirmed for several months as contest administrators conduct a full, line-by-line audit of all submitted contact logs to verify compliance with contest rules and eliminate invalid entries. Team leadership extended formal public gratitude to local partners that made their 2024 operation possible, specifically thanking Elite Island Resorts for providing discounted, convenient accommodation for the traveling international team members, and the Antiguan Ministry of Information Communication Technologies for streamlining the process to secure all required temporary telecommunications licenses to run their high-power contest transmissions legally on local soil.
-
RvC TAS roept personeel dinsdag op; dienstverlening donderdag hervat
On October 26 at 19:14 local time, the Supervisory Board (Raad van Commissarissen, RvC) of the Telecommunications Authority Suriname (TAS) announced a series of operational adjustments following a landmark court decision that ousted former director Wendy Jap-A-Joe from her post. The ruling, delivered by District Judge Robert Praag on Monday, formally bars Jap-A-Joe from exercising any executive or representative powers on behalf of the telecom regulator, and mandates that she hand over all administrative, operational, financial and institutional records and responsibilities to the appropriate governing body. The legal foundation for the court’s decision stems from the fact that Jap-A-Joe’s official statutory appointment term expired on October 19, stripping her of all legitimate authority tied to her former director role as of October 20. The verdict has been declared provisionally enforceable, meaning all outlined measures take immediate legal effect, no pending appeals can delay implementation. Headed by chair Emanuel Scheek, the TAS Supervisory Board has issued a formal public notice addressing all staff, telecom industry stakeholders and relevant third parties to clarify the path forward for the regulator. Per Article 4(2) of the Surinamese Telecommunications Facilities Act, the full Supervisory Board will collectively assume interim executive control of TAS in the absence of a formally appointed director and deputy directors. All TAS personnel have been instructed to report to the agency’s office at the intersection of Flustraat and Naarstraat, address 35, at 9 a.m. on Tuesday, October 27. During this mandatory gathering, the Supervisory Board will hold introductory sessions with all team members, outline critical organizational protocols and operational guidelines, before resuming internal workflow immediately afterward. The board has confirmed that full regular public services, including support for license holders and other industry stakeholders, will be fully restored starting Thursday, October 29. The RvC has pledged to deploy every available resource to safeguard uninterrupted administrative and operational continuity for the national telecom regulatory body, to avoid disruptions to the country’s digital communications ecosystem. The full official public statement from the Supervisory Board is available for public download via the attached document “Algemene_mededeling_RvC.pdf”.
-
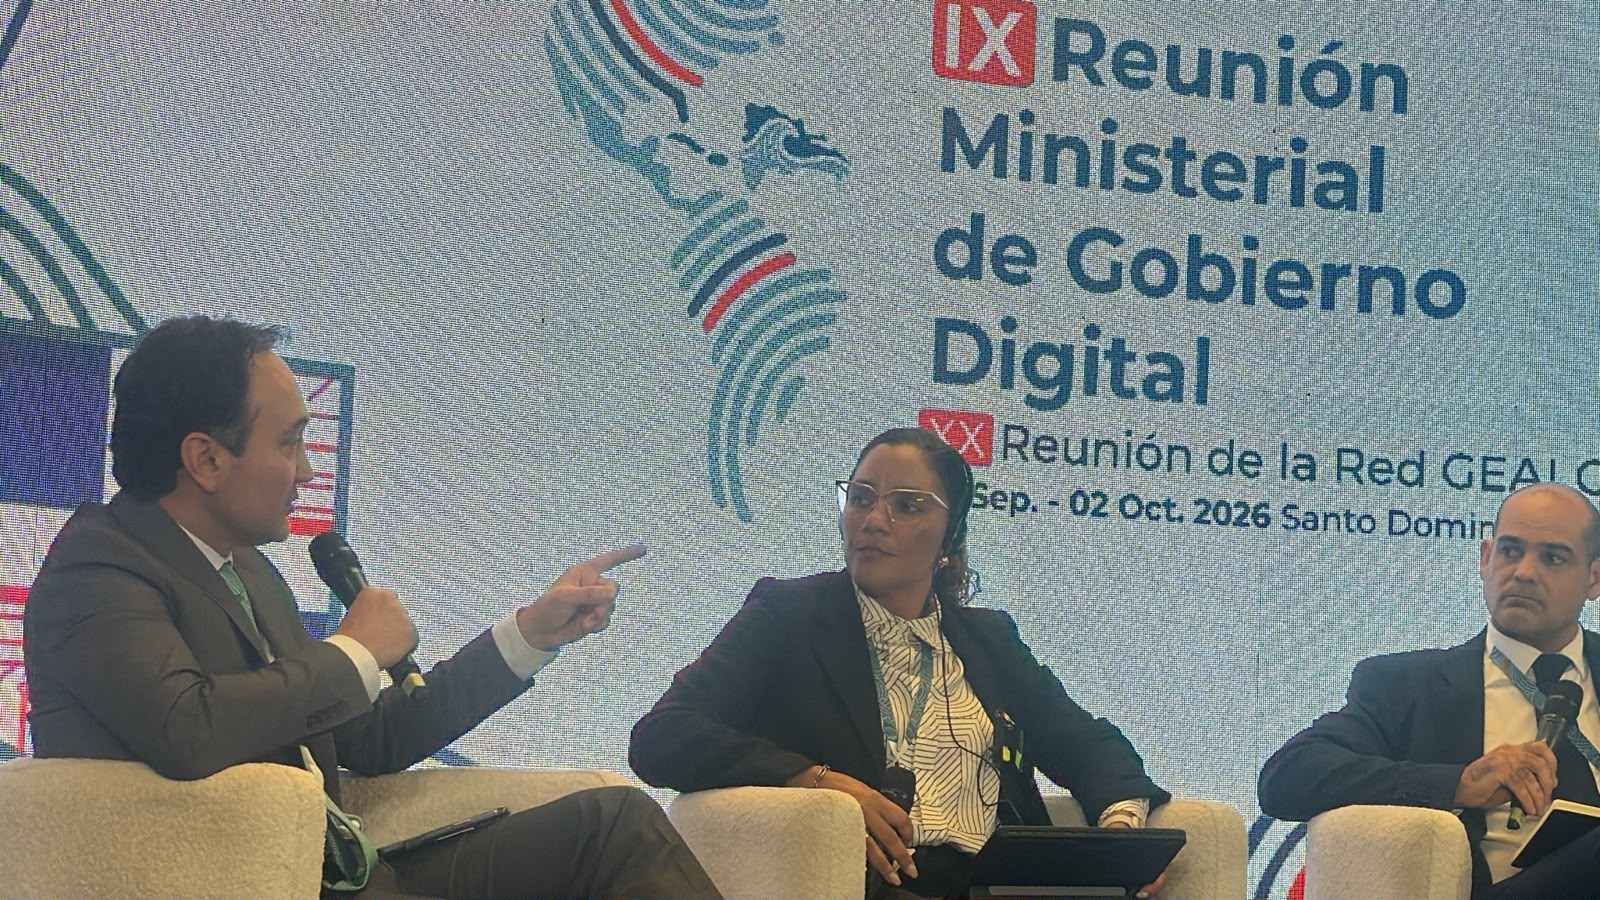
Antigua and Barbuda ICT officials attend regional forum on improving digital government services
A senior delegation from Antigua and Barbuda’s Ministry of Information Communication Technologies, Utilities and Energy recently took part in the 2026 Regional Digital Public Infrastructure (DPI) Forum hosted in Santo Domingo, Dominican Republic, as part of a broader regional push to modernize public service delivery through robust digital frameworks. The two-member national delegation comprised Isoke Perry, Director of the country’s eGovernment division, and Desiree Zachariah, Manager of Business and Data Analysis, who joined over 150 cross-sector stakeholders at the event spanning government leadership, global development partners, tech practitioners and digital policy specialists. Over the course of the multi-day gathering, participants dove deep into actionable strategies to build national digital systems that are secure, cross-compatible, and accessible to all segments of the population, with dedicated sessions covering core DPI building blocks: universal digital identity frameworks, integrated digital payment rails, standardized cross-agency data exchange protocols, robust cybersecurity guardrails, open-source digital public goods, tamper-proof verifiable credentials, cross-government system interoperability, and sustainable financing models for long-term digital infrastructure rollout. For the Antigua and Barbuda delegation, the forum served as a targeted knowledge-sharing platform to identify proven, context-appropriate solutions that align directly with the country’s ongoing digital transformation roadmap, which prioritizes expanded eGovernment service access, more rigorous and ethical management of public sector data, and smoother cross-departmental coordination across government agencies. One of the highest-priority discussion tracks focused on digital interoperability, a foundational design principle that allows disparate government information systems to share verified data quickly and without security risks. When deployed effectively, these interconnected systems eliminate redundant data entry requirements, cut down on unnecessary administrative paperwork, and create far more streamlined experiences for citizens and business owners seeking services across multiple government departments. The delegation’s participation also underscores the government’s recognition that successful, user-centric digital service delivery cannot exist in isolation: it must be paired with rigorous, well-resourced data management and analytical capacity to ensure systems deliver tangible public value. For Antigua and Barbuda, a fully realized national DPI ecosystem stands to deliver a host of measurable quality-of-life improvements for local citizens, residents, and registered businesses alike: fewer mandatory in-person visits to government office locations, no repeated submission of identical personal information across separate agencies, drastically faster turnaround times for permit and benefit applications, and expanded access to critical public services via digital channels for communities that have historically faced geographic or logistical barriers to in-person support. Forum attendees emphasized that unlocking these full benefits will demand coordinated long-term action: intentional strategic planning, targeted institutional capacity building, sustained public and private investment, upskilling for public sector workforces, and ironclad regulatory safeguards to protect personal data privacy and defend digital systems from evolving cyber threats. A standout highlight of the event was a series of on-the-ground case study presentations from Dominican Republic government officials, who walked delegates through their country’s award-winning national digital government architecture, including its fully operational interoperability framework and the widely adopted “Soy Yo RD” verifiable digital identity credential program, offering a concrete, real-world blueprint for other Caribbean nations to adapt as they build out their own DPI ecosystems.
-
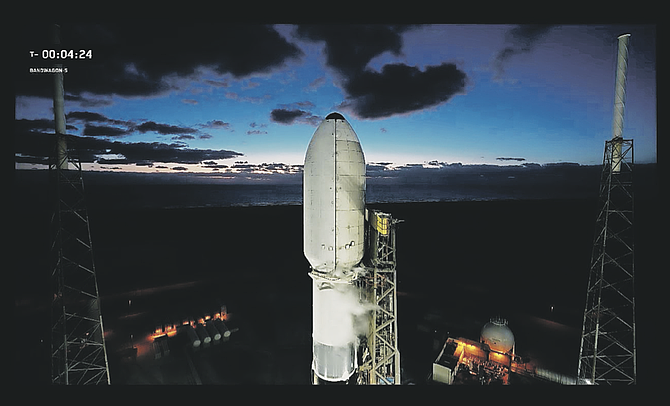
Tomorrow.io launches polar orbit satellites to improve weather monitoring across The Bahamas
Leading weather technology firm Tomorrow.io, a longstanding strategic collaborator with the Bahamas Aviation, Climate and Severe Weather Network (BACSWN), has successfully deployed a new generation of advanced low-Earth orbit (LEO) weather monitoring satellites into polar orbital trajectory. The satellite cluster was carried aloft aboard SpaceX’s Bandwagon-5 launch vehicle, which lifted off from the Cape Canaveral Space Force Station launch facility in Florida. The new satellite constellation delivers a transformative upgrade to weather surveillance capabilities across the Bahamas’ 173,000 square miles of territorial airspace and maritime zones, cutting the previously standard three-hour data refresh interval to less than 60 minutes. This substantial performance leap drastically boosts real-time situational awareness for local aviation, emergency response agencies, and public safety stakeholders, eliminating critical lag times that previously hindered timely severe weather preparedness. Per official details published on Tomorrow.io’s public web portal, the company’s end-to-end weather and climate security platform is purpose-built to equip private sector operators, national government agencies, and sovereign nations with actionable, hyper-local forecasting data that allows stakeholders to anticipate, plan for, and mitigate the disruptive operational impacts of extreme weather events well before adverse conditions unfold.
-
Ernstige cyberdreiging treft wereldwijd websites; ook Starnieuws neemt voorzorgsmaatregelen
A newly disclosed pair of critical security vulnerabilities in the widely used programming language PHP has sent shockwaves through the global digital community this Wednesday, triggering widespread alarm among website and digital service administrators worldwide.
The two flaws, rated 9.2 out of 10 on the industry standard criticality scale, grant unauthenticated remote attackers the ability to execute arbitrary code on vulnerable servers under specific conditions. This puts sensitive data including user personal information, core website databases, and the continuous operation of online services at severe risk of compromise. Given PHP’s near-ubiquitous use across the internet — powering everything from front-end websites to back-end data processing systems — the threat extends to organizations of all types: government agencies, private businesses, financial institutions, media outlets, and nonprofits across every continent.
In response to the escalating threat, organizations in multiple countries have proactively taken vulnerable websites offline as a precautionary measure. The PHP development security team has already released emergency security patches that address both vulnerabilities, which are tracked under the CVE identifiers CVE-2026-109618 and CVE-2026-109619. Global cybersecurity agencies have issued urgent advisories urging all organizations that run PHP-powered systems to immediately audit their infrastructure and install the available patches as quickly as possible. For entities that cannot deploy updates right away, agencies recommend temporarily disconnecting vulnerable systems from the public internet as a stopgap protection.
Cybersecurity authorities in the United Kingdom and the Netherlands have additionally warned that the risk extends beyond public-facing websites. Third-party vendor tools and back-end enterprise applications also often run on PHP, meaning even organizations that do not operate public websites may still face exposure to the flaw.
The warning has also reached Suriname, where government agencies, banks, businesses, media outlets and other organizations have become increasingly reliant on digital systems for daily operations. Local outlet Starnieuws confirmed that its technical team has already rolled out multiple preventive measures to mitigate potential security risks in response to the global alert.
Cybersecurity analysts note that this incident underscores the deep interconnected fragility of global digital infrastructure. A single critical flaw in a widely used programming language can create cascading risks for organizations across borders and sectors. Crucially, the release of security patches does not eliminate the threat immediately: websites and systems remain vulnerable until the updates are actually applied.
Global cybersecurity officials emphasize that digital security is far more than a purely technical issue. It directly impacts the accessibility of public services, the protection of personal privacy, and the continuity of critical services including news reporting. That is why rapid action by website administrators is so critical. For end users, officials add that a temporarily unavailable website is not automatically evidence of a successful cyberattack — in most cases, it is a deliberate precaution to stop an attack from happening in the first place.
-
NOTICE : The BRH face the phenomenon of cyberattacks
Cybersecurity threats targeting global financial systems have grown to unprecedented levels over the last half-decade, and Haiti’s national financial infrastructure has not escaped this growing risk, according to the top official at the Bank of the Republic of Haiti (BRH).
In a public notice issued October 21, 2026, BRH Governor Donald Gabriel warned that local financial institutions have increasingly become primary targets for malicious cyber actors, amid a regional and global surge in large-scale attacks on banking and financial ecosystems. Despite the rising threat, Gabriel emphasized that Haiti’s financial sector already operates under structured regulatory frameworks that require the deployment of robust, secure information systems designed to mitigate the potential damage of cyber incidents.
Since 2023, the BRH has prioritized upgrading the nation’s financial cyber defenses through a multi-pronged strategy focused on capacity building, proactive training, and widespread awareness campaigns for sector stakeholders. The central bank’s approach combines investment in advanced defensive technologies with training to encourage responsible risk mitigation practices among financial sector leaders, with the ultimate goal of strengthening the resilience of core operational systems against evolving cyber threats.
As part of its regulatory oversight mandate, the BRH also enforces requirements for all licensed financial institutions to implement comprehensive safeguards for customer personal and financial data. A key new policy clarification issued in the notice bans all domestic financial bodies from engaging in ransom negotiations with cybercriminals, even in the aftermath of a successful breach that locks organizations out of critical systems.
Instead, the central bank mandates that any institution targeted by a cyberattack must immediately activate pre-approved contingency and business continuity plans to maintain essential services. At the same time, institutions are required to conduct detailed forensic analysis of digital traces left by attackers to identify vulnerabilities and strengthen system defenses against future incidents. The notice reaffirms the BRH’s commitment to protecting the stability of Haiti’s financial system and safeguarding customer assets amid growing global cyber risks.