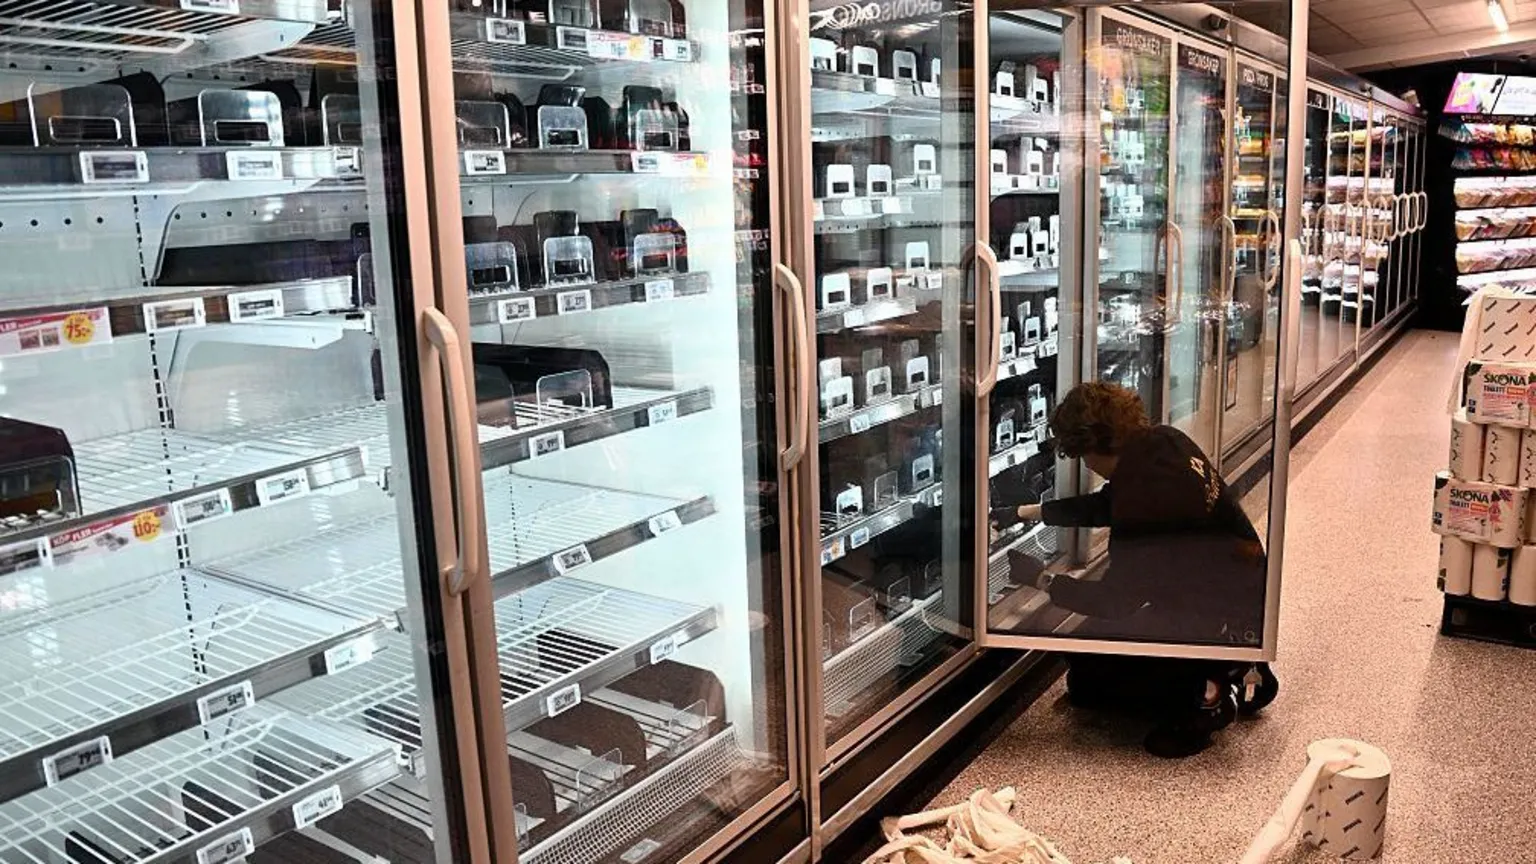
A widespread cyberattack that infiltrated connected freezer management systems across dozens of European supermarket chains has caused cascading operational disruptions throughout the United Kingdom’s multi-billion-pound meat processing and distribution sector, industry authorities confirmed this week. The malicious campaign was designed to exploit unpatched vulnerabilities in internet-enabled temperature monitoring platforms that thousands of grocery retailers rely on to maintain safe, regulated storage conditions for frozen and chilled perishable goods. Initial investigations indicate threat actors gained remote access to centralized freezer control panels across 12 European Union member states and the UK earlier this month, triggering unintended shutdowns and temperature fluctuation alerts that left distribution teams scrambling to prevent mass product spoilage. For UK meat processors, the attack created significant bottlenecks: dozens of retail partners paused incoming meat shipments for 48 to 72 hours while IT teams verified the integrity of their cold storage infrastructure, leaving hundreds of tons of fresh and frozen lamb, beef, and pork products stranded at processing facilities and regional distribution hubs. The UK National Cyber Security Centre (NCSC) has issued an urgent advisory to all food and beverage supply chain operators to conduct immediate vulnerability scans of their connected industrial control systems, noting that food and agriculture infrastructure has become an increasingly high-priority target for cybercriminal groups seeking ransom payments. Industry trade bodies are now working with government cybersecurity teams to roll out emergency security patches and coordinated response protocols to prevent further disruptions, as preliminary estimates suggest the attack could cost the UK meat sector up to £20 million in wasted product and lost revenue in the first two weeks alone.
UK meat industry hit by cyber-attack which targeted European supermarket freezers